
Continuum GRC: OCC Cyber Work Program Makes Control Mapping an Examiner Readiness Priority
Continuum GRC Infinity Cog Logo
Continuum GRC: OCC Cyber Work Program Makes Control Mapping an Examiner Readiness Priority
The agency added no new procedures, but its structure reinforces the value of mappings, accountable ownership, and evidence that is followed across frameworks.
OCC Bulletin 2026-48 says the agency updated the work program’s structure and references to align with evolving NIST CSF categories and subcategories. The OCC states that it added no new procedures, changed no procedures, and created no new regulatory expectations. Banks are not expected to use the examiner work program as their own preparedness assessment, and the agency continues to permit institutions to choose among standardized tools and frameworks.
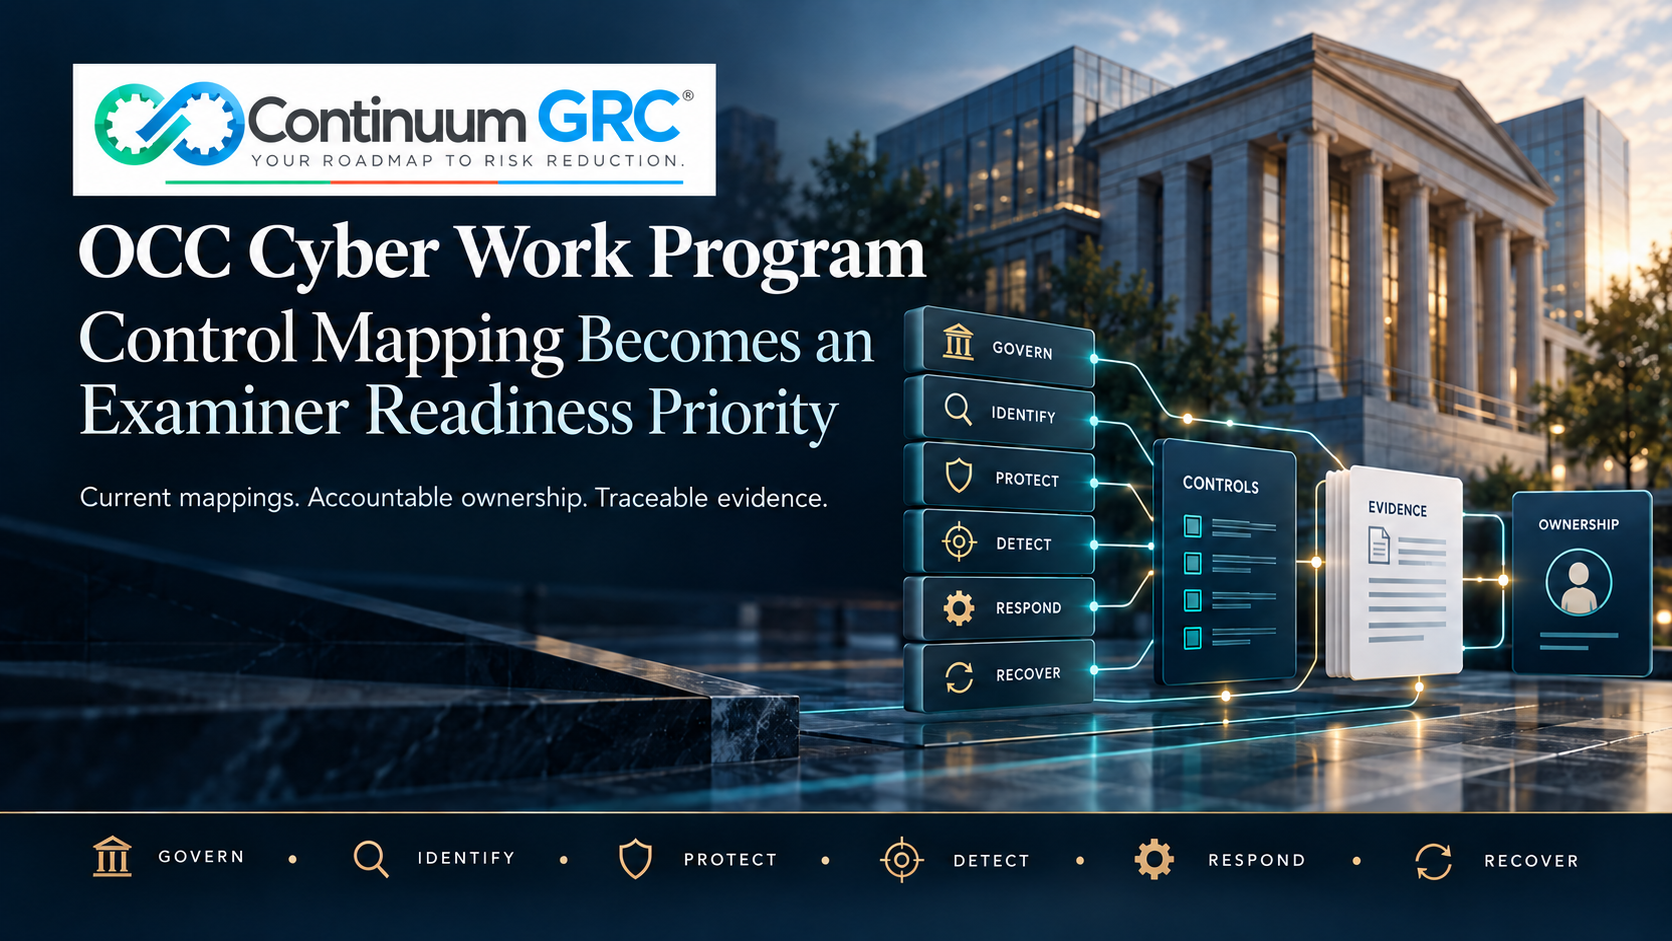
Even without a new mandate, the update matters operationally. The work program is used in risk-based supervision and maps to the FFIEC Information Technology Examination Handbook, OCC supervisory materials, and common cybersecurity frameworks. Its structure spans the NIST CSF functions Govern, Identify, Protect, Detect, Respond, and Recover, creating a practical lens through which examiners can follow governance, implementation, and evidence across the cyber program.
A September 29 speech by Federal Reserve Vice Chair for Supervision Michelle Bowman reinforced the executive context for that work. She pointed to significant cyber events affecting community banks, described threats including ransomware, business email compromise, vendor data breaches, and AI-enabled attacks, and emphasized board and senior-management risk ownership, employee training, and periodic incident-response testing.
Banks should use the moment to validate, not merely refresh, their crosswalks. Each mapped control should identify an accountable owner, the authoritative policy or procedure, the systems and third parties in scope, the evidence proving operation, and the most recent test or remediation decision. Where one artifact supports several frameworks, organizations should preserve the source evidence and document the mapping logic instead of maintaining disconnected copies that can drift.
For community banks in particular, a scalable evidence model can support proportionate examination readiness. The objective is not to reproduce the OCC’s work program. It is to make the institution’s own risk decisions, control performance, exceptions, and corrective actions easy to trace when supervisors ask how cybersecurity preparedness matches the bank’s size, complexity, and risk profile.
“A framework crosswalk is useful only when it leads to living evidence. Banks should be able to move from an examiner’s question to the responsible owner, the control as designed, the proof that it operated, and any open remediation without rebuilding the story for every review.” - Michael Peters, Founder and CEO
About Continuum GRC
Continuum GRC is the enterprise SaaS platform developed by Lazarus Alliance that automates and accelerates Governance, Risk, and Compliance (GRC) programs. Built on the proprietary IT Audit Machine® (ITAM) and A.ITAM frameworks, Continuum GRC is FedRAMP Authorized at the Moderate baseline and delivers continuous control monitoring, automated evidence collection, risk scoring, dashboards, and AI-powered assessment capabilities through AITAMBot. Organizations use Continuum GRC to streamline CMMC, FedRAMP, SOC 2, NIST, ISO, PCI DSS, CJIS, and other frameworks—reducing audit timelines, improving accuracy, and enabling faster authorization and certification outcomes.
Michael Peters
Continuum GRC, Inc.
+17628224174 ext.
email us here
Visit us on social media:
LinkedIn
YouTube
X
Self Attestation VS Third Party Attestation
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
